London, U.K., September 23, 2026
- Gartner client? Log in for personalized search results.
Gartner Security & Risk Management Summit 2026 London: Day 2 Highlights
It’s not too late to join the conference
Overview
We are bringing you news and highlights from the Gartner Security & Risk Management Summit, taking place this week in London. Below is a collection of key announcements and insights coming out of the conference. You can read the highlights from Day 1 here.
On Day 2 of the conference, we are identifying seven critical threats that CISOs need to have on their radar, addressing the threat quantum poses to cybersecurity and exploring the future of cyber in 2030. Be sure to check this page throughout the day for updates.
Key Announcements
Turbulence Report 2026: 7 Forces That Will Threaten Your Organization’s Future
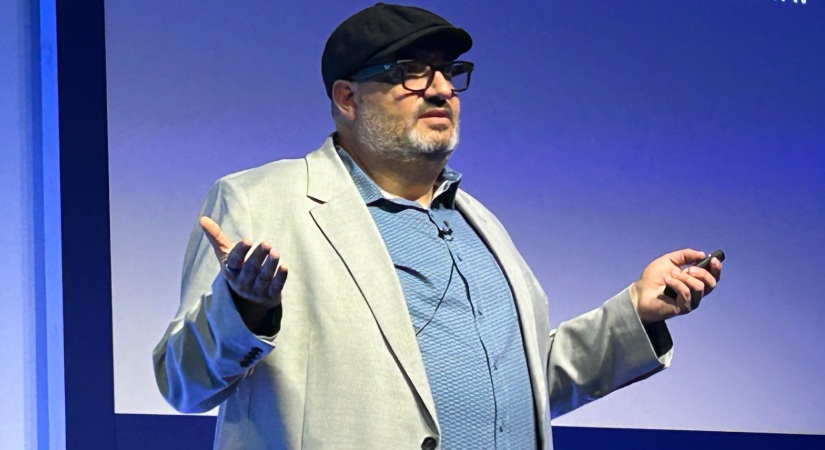
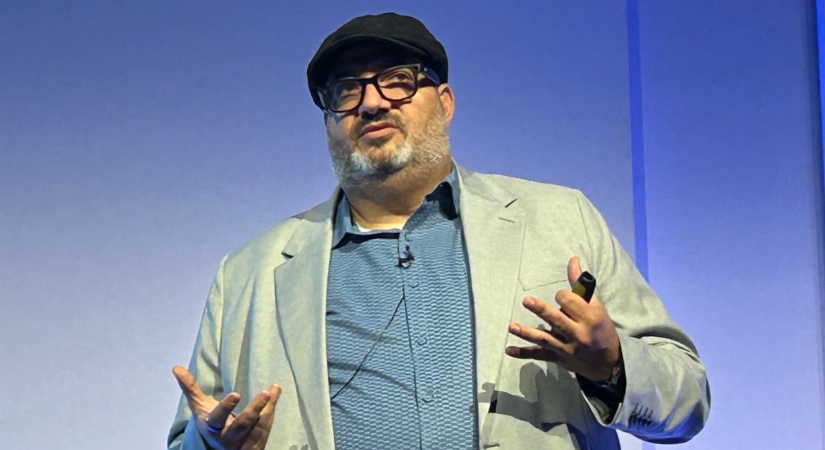
Presented by Marty Resnick, VP Analyst, Gartner
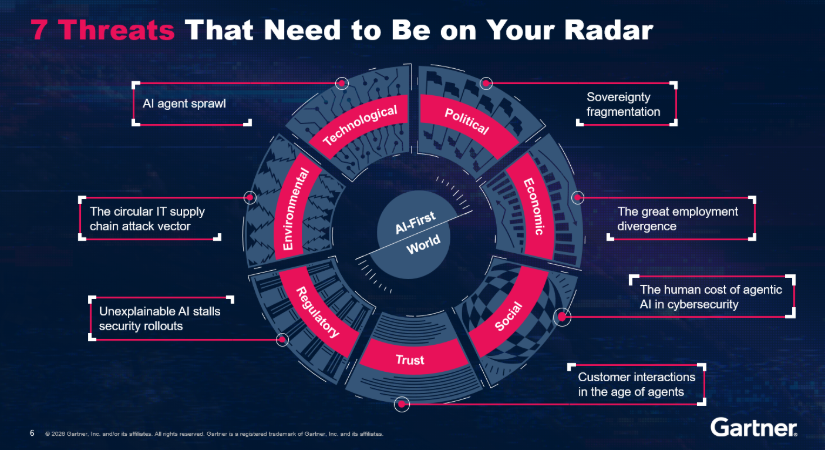
The security landscape is constantly evolving and becoming more complex, with threats emerging across all areas of what Gartner refers to as the Tapestry framework: technology, politics, economics, social factors, trust, regulatory and environmental forces (TPESTRE). In this session, Marty Resnick, VP Analyst at Gartner, discussed the seven forces that could threaten an organization’s future.
Key Takeaways
To successfully lead their organizations in an AI-first world, CISOs must understand and address seven emerging threats that are reshaping the cybersecurity landscape:
- AI agent sprawl
- Sovereignty fragmentation
- The human cost of agentic AI in cybersecurity
- The great employment divergence
- Customer interactions in the age of agents
- Unexplainable AI stalls security rollouts
- The circular IT supply chain attack vector
Gartner predicts that by 2028, ungoverned AI agent abuse will drive 25% of enterprise breaches, mandating the adoption of zero-trust governance and agent-specific kill-switches.
Gartner predicts that by 2028, 30% of multinational organizations will be forced to restructure their AI architecture to comply with multipolar national sovereignty mandates, increasing operational costs by 20%.
“Organizations that enable their employees to grow with the adoption of AI will see greater growth and innovation than those that choose to eliminate staff today with the expectation that AI will be a reliable replacement.”
Journalists can receive additional information and/or request an interview with Marty Resnick by contacting Laurence Goasduff at laurence.goasduff@gartner.com.
Stopping the Quantum Threat: PQC in Three Waves
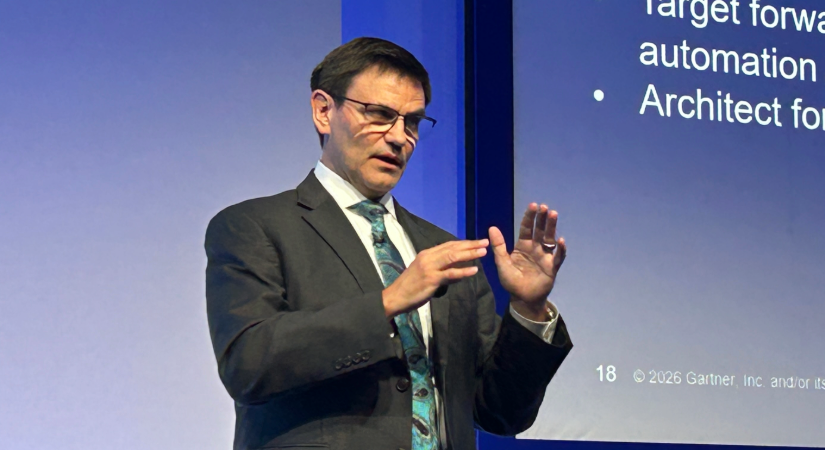
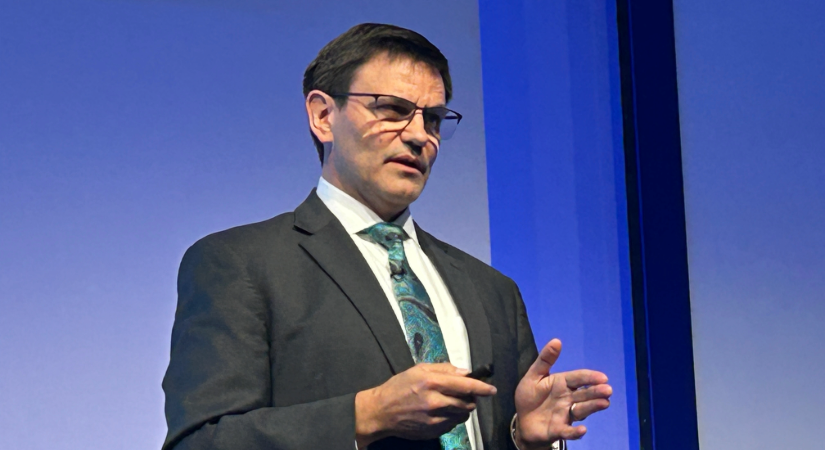
Presented by Thomas Lintemuth, Director Analyst, Gartner
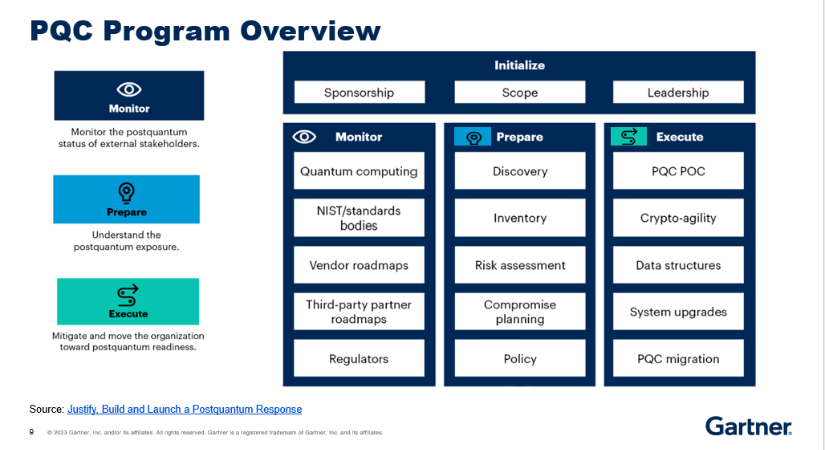
The clock is ticking on current cryptographic infrastructure. With the advent of large-scale, fault-tolerant quantum computers looming, the algorithms that organizations rely on today will be rendered obsolete, leaving digital communications vulnerable. In this session, Thomas Lintemuth, VP Analyst at Gartner, discussed the three waves of cryptography which security leaders will need to upgrade before Q-day hits.
Key Takeaways
“Quantum computers pose a significant threat to cybersecurity primarily because they can break many of the cryptographic algorithms currently used to secure the digital world.”
“Gartner predicts that a sufficiently powerful quantum computer could arrive by the end of the decade. It is not so much a matter of if, but when.”
“Post quantum cryptography (PCQ) will come at us in three waves. Security leaders need to be prepared and have a plan to address the waves as they hit.”
- Wave 1: Strengthen symmetric encryption and migrate to postquantum key exchange.
- Wave 2: Upgrade private PKI and the hardware security modules (HSMs) that underpin it. Monitor public PKI.
- Wave 3: Migrate digital signatures, prioritizing long-lived use cases, and budget for potential hardware upgrades.
“Migration to post-quantum cryptography will happen regardless of if quantum computing becomes a real threat or not.”
Journalists can receive additional information and/or request an interview with Thomas Lintemuth by contacting Laurence Goasduff at laurence.goasduff@gartner.com.

It’s not too late to join the conference
More updates from the conference will be shared throughout the day.


About Gartner
Gartner (NYSE: IT) delivers actionable, objective business and technology insights that drive smarter decisions and stronger performance on an organization’s mission-critical priorities. To learn more, visit gartner.com.