Written policies cannot control autonomous actions at machine speed.
- Gartner client? Log in for personalized search results.
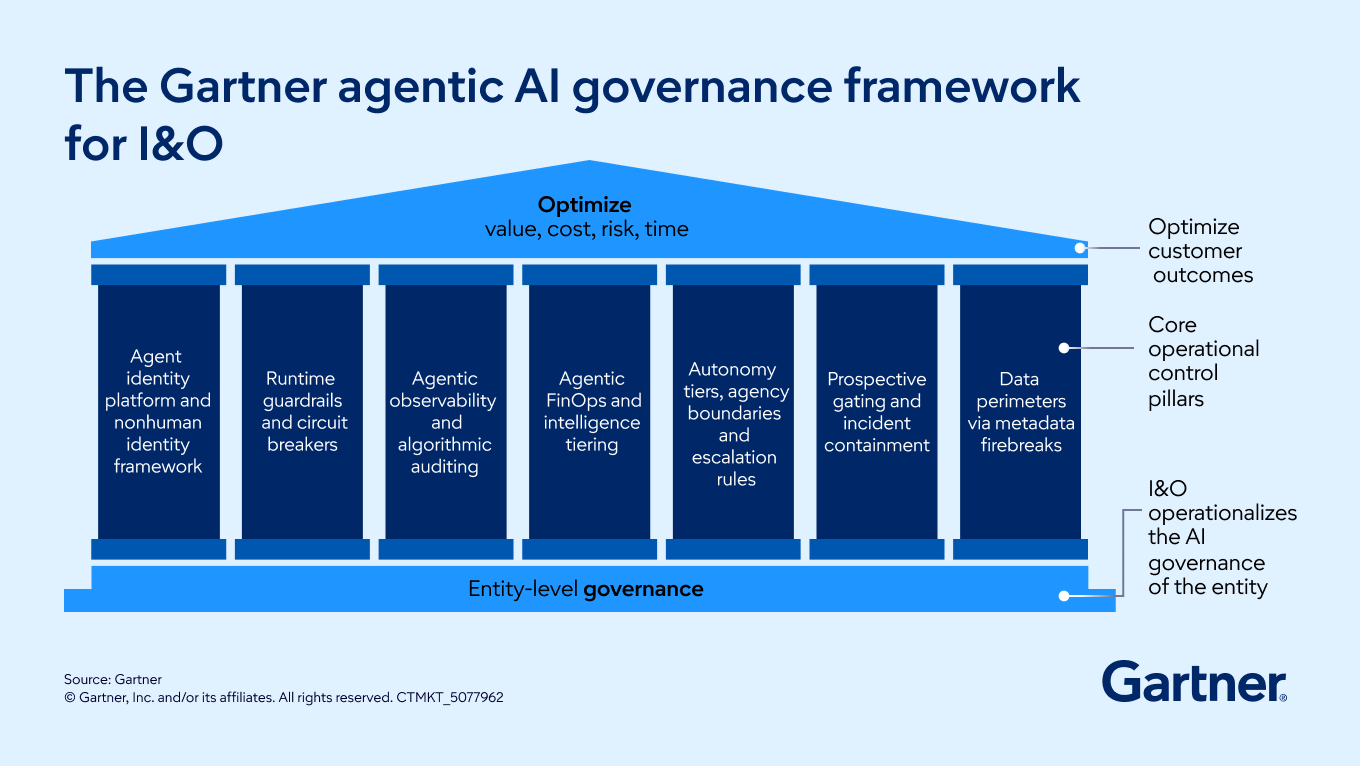
The governance gap is the real agentic AI risk
Organizations are approaching agentic AI with governance models designed for traditional software and human decision making. The problem is that AI agents do not simply generate content. They can execute multistep workflows, modify system states and act autonomously at machine speed. The most significant challenge is the gap between written corporate policies and the runtime controls needed to enforce them.
Agentic workflows rely on probabilistic reasoning, making them susceptible to decisions that can trigger operational disruption, unauthorized purchases, excessive token consumption or uncontrolled resource usage. Gartner predicts that by 2029, at least 70% of organizations with production agentic AI in I&O will experience a material service, security or cost incident linked in part to insufficient runtime controls. “Written corporate policies cannot physically stop an agent from making a destructive error,” says George Spafford, Vice President Analyst at Gartner.
You might also like this webinar: 2026 Technology Adoption Roadmap for Infrastructure and Operations
Governance must move from policy to runtime control
Traditional governance depends on human approvals, static policies and after-the-fact oversight. Agentic AI requires a fundamentally different approach focused on governing autonomous decisions and execution. Heads of I&O should embed controls directly into the operational environment so agents can operate safely within defined boundaries.
Treat agents as governed identities
Organizations cannot govern autonomous systems they cannot see. Gartner recommends establishing an agent identity platform and nonhuman identity framework that treats every internal and third-party agent as a distinct identity with clearly defined ownership and access rights.
This identity-first approach helps reduce the risk of shadow AI while creating accountability for autonomous actions. Organizations should maintain a centralized registry of agents, classify them as nonhuman identities and apply dynamic least-privilege access controls. Rather than relying on static credentials, agents should receive temporary access that is revoked when tasks are complete. This ensures organizations can attribute every autonomous action to a responsible human owner and maintain the auditability required for governance and compliance.
Replace manual oversight with active guardrails
The shift from GenAI to agentic AI expands risk because agents can take action, not just generate responses. Incorrect reasoning can lead to destructive commands, logic loops, unauthorized transactions and significant cost overruns. To reduce these risks, organizations should move beyond policy documents and deploy active runtime controls. They should also implement stateful circuit breakers and maintain a strict separation between AI reasoning and execution. In this model, agents can propose actions, but a separate control layer evaluates those actions before execution. This approach allows organizations to block unsafe behavior before it affects production environments and helps prevent runaway activity from consuming resources or disrupting operations.
Build visibility, financial controls and escalation paths
Traditional monitoring tools focus on infrastructure health but provide little insight into why an autonomous system made a decision. Heads of I&O should shift to agentic observability and algorithmic auditing that capture reasoning chains, selected actions and decision history in immutable records.
Financial governance also becomes more important because agentic workloads can consume resources unpredictably. Organizations must implement intelligence tiering, dynamic budgets and automated financial controls that stop execution when limits are exceeded. Finally, leaders should define autonomy tiers and escalation rules based on risk. Low-risk activities may operate autonomously, while high-impact and irreversible actions should require explicit human approval. Governance should combine deterministic controls, human oversight and incident containment capabilities so organizations can quickly isolate rogue behavior when necessary.
AI governance FAQs
What is the biggest governance challenge with agentic AI?
The primary challenge is the governance gap between written policies and the runtime controls required to manage autonomous systems. Traditional policies cannot reliably prevent unsafe actions once an AI agent begins executing tasks.
Why are runtime controls important for agentic AI?
Agentic AI can modify system states and execute multistep actions autonomously. Incorrect reasoning can cause operational disruption, financial losses, compliance issues and security incidents. Runtime controls help prevent these outcomes before execution occurs.
What governance actions should heads of I&O prioritize?
Heads of I&O should establish an agent identity platform, deploy runtime guardrails, operationalize agentic FinOps and enforce data perimeters through governed context layers and zero-trust validation.
Attend a Conference
Join Gartner analysts and your peers to accelerate growth
Gather alongside I&O leaders in Las Vegas to gain insight on emerging trends, receive one-on-one guidance from Gartner experts and create a strategy to tackle your priorities head-on.
8 – 10 Dec 2026
Gartner IT Infrastructure, Operations & Cloud Strategies Conference
Las Vegas, NV
Drive stronger performance on your mission-critical priorities.